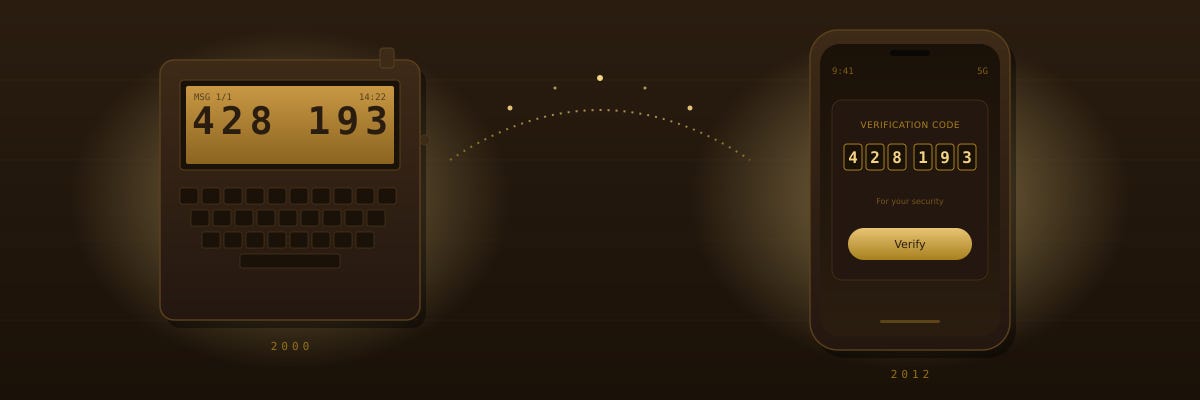
It was 1999, maybe early 2000. We were pitching a VC - I forgot which one - and there was an EIR in the room: Tim Howes, one of the authors of LDAP. Tim had a two-way BlackBerry pager. We spent the first time of the meeting passing it around, marveling at it.
We were building what would later be called an SSL VPN. Prospects kept asking us to integrate with RSA SecurID and VascoID, those little keychain fobs that displayed a rotating six-digit code. Difficult for a startup to get a deal with. Expensive to deploy. Annoying to lose. A logistics problem for IT.
Watching Tim’s pager, the idea hit me: send the second factor to the device people already carry. No fob, no shipping, no replacement cycle. Just a number, pushed to a thing in your pocket, that you type into a login prompt.
I pitched it internally. The kitty was empty, we were a startup, not a patent factory, and our design partners pushed back. The pager network wasn’t encrypted. The carrier could see the code. Not secure enough. They weren’t wrong on the facts, and it didn’t matter, because facts about the threat model weren’t what was going to decide this.
We didn’t file. A decade later, every bank, every SaaS, every email provider on earth was sending six-digit codes to phones. The thing that was “not secure enough” in 2000 became the global default by 2012.
I think about that often. Not because of the patent. Patents are mostly lottery tickets and lawyer fees, but because of why the market changed its mind. And here’s the cynical part.
2FA is not, primarily, a security feature. It’s an account-sharing prevention feature wearing a security costume.
If you actually wanted to secure a login, you’d use a hardware key or a passkey bound to a device’s secure enclave. SMS 2FA is famously breakable. SIM-swap attacks have been documented for over a decade, and NIST has been warning against SMS as a second factor since 2016. Every serious security team knows this. SMS 2FA is still what most consumer services use, because the security isn’t the point.
What SMS-to-phone actually does, very effectively, is bind a session to a specific human holding a specific SIM. It makes it annoying to share your Netflix login with your daughter in another city. It stops bots from running credential-stuffing attacks at scale. Two of those three things have nothing to do with protecting you. They protect the vendor’s revenue and infrastructure costs. Those are legitimate business problems. The little “for your security” line in the prompt is just not the whole story.
“Send the code to a pager” didn’t fail in 2000 because the pager network was insecure. It failed because nobody had yet figured out they wanted account-sharing prevention badly enough to deploy infrastructure for it. The crypto didn’t improve between 2000 and 2012. The business model caught up.
Why I’m thinking about this now
I’m building Yovico, a multi-persona AI simulation platform. Founders use it to practice pitches with an AI playing a seed VC. Operators red-team strategy with an AI playing a Gartner analyst. The personas have persistent memory,they remember what you tried last time, where you got pushback, what you’ve been working on.
And I can already see the day I’m going to face the same pressure every B2B SaaS company faces. One login fans out to a whole founding team. Then a whole accelerator cohort. Then a whole VC portfolio. API costs go vertical. Unit economics get ugly. And someone, maybe an investor, maybe an advisor, probably both, is going to tell me to add 2FA for security.
I want to say the quiet part now, while it costs me nothing.
When Yovico eventually binds sessions to humans, it won’t be because I’m worried about your account getting hacked. It’ll be because the persona memory only works if it’s yours. If Igor practices his Sequoia pitch and his cofounder logs in next and practices the same pitch, and the persona blends them into one mushy graph of “things this account has done”, the product breaks. The value of a persistent multi-persona simulation is that it tracks one mind over time, not an account.
So yes, eventually there will be identity binding. And yes, it will look a lot like the access control every other SaaS company runs. But the reason is that the memory is per-human because the product is per-human, not that I’m shielding you from threats that mostly aren’t there.
The next time a service makes you set up 2FA and tells you it’s for your security, ask who’s actually being protected. Usually it’s both of you. Usually the vendor more than you. They could just say so.